

A help desk ticket that creates a standard user account is not the same as a request for domain admin rights. Treating both as an identity problem is how organizations end up with broad privileges, thin audit trails, and a lot of uncomfortable questions after an incident. PAM versus IAM is not a contest between competing tools. It is a decision about which access risk you need to control, and how precisely you need to control it.
For MSPs, MSSPs, VARs, and SIs, the distinction matters twice. You have to protect the customer environment, and you have to protect the privileged access your own engineers need to support it. The right architecture gives technicians enough access to do real work without leaving permanent keys under every customer’s doormat.
PAM versus IAM: the practical difference
Identity and Access Management, or IAM, governs digital identities and their routine access to systems, applications, and data. It answers foundational questions: Who is this person? What role do they have? What are they allowed to access? How do we verify them? And what happens to that access when their job changes or ends?
Privileged Access Management, or PAM, is a security discipline within the broader identity picture. It focuses on accounts and sessions with elevated permissions: domain administrators, cloud tenant administrators, root users, database administrators, service accounts, emergency accounts, and third-party support credentials. PAM answers a more consequential question: When someone has the power to change, disrupt, or extract critical systems, how do we limit, monitor, and prove that use?
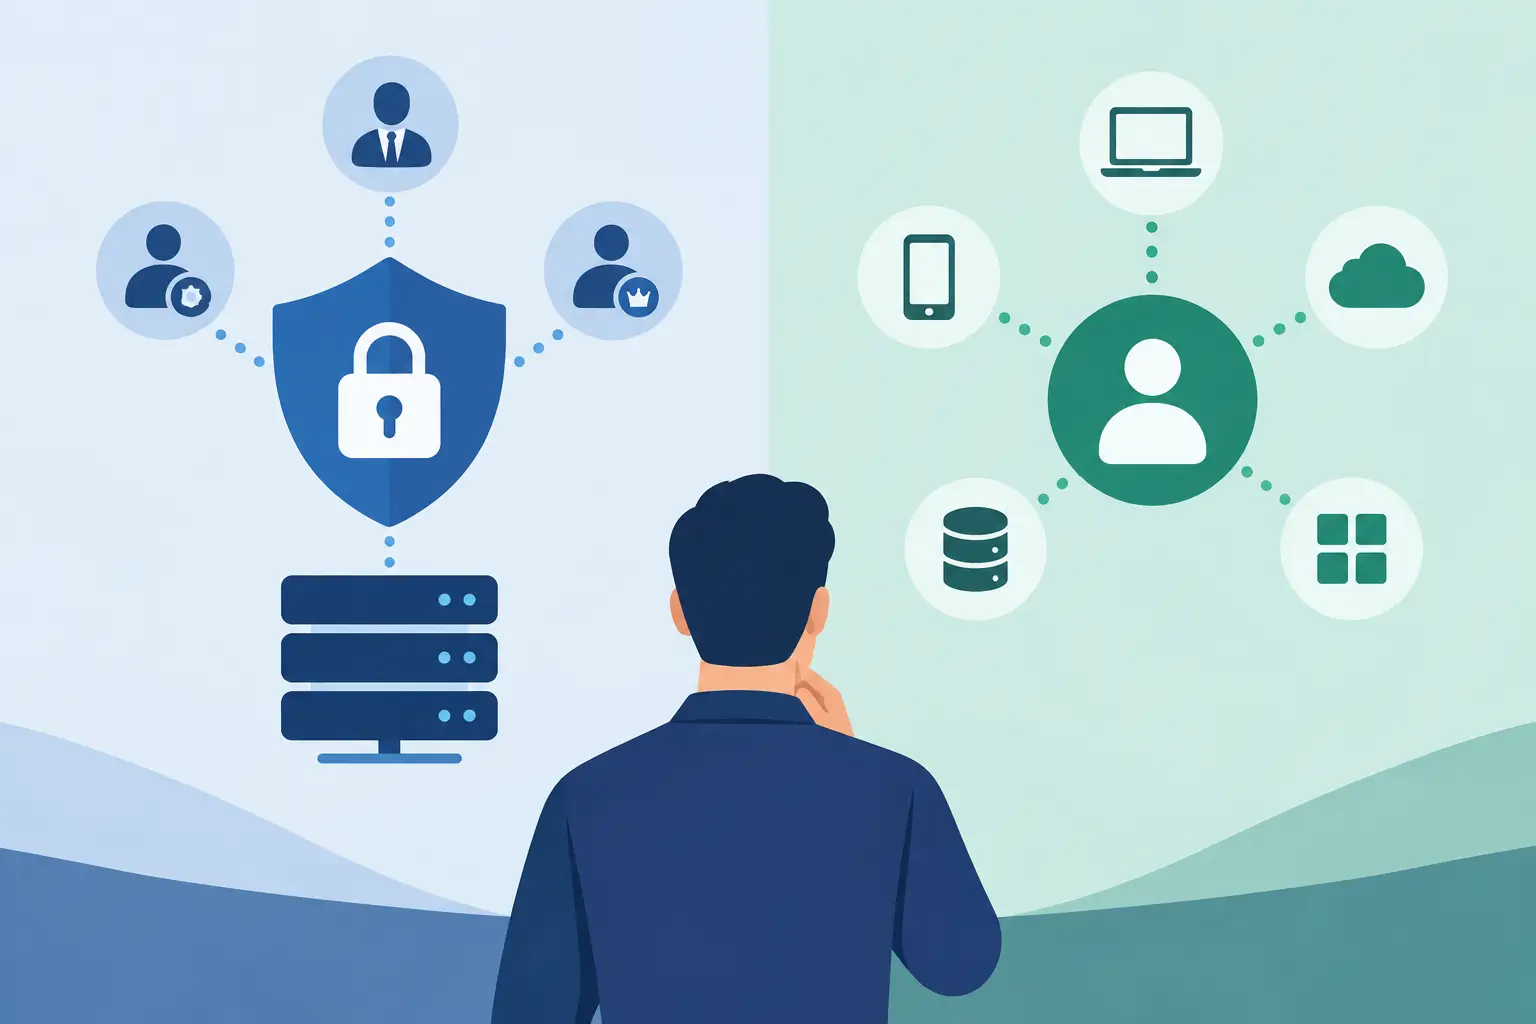
IAM is the front door and the badge system. PAM is the controlled room behind the badge reader, with a camera, a sign-out log, and limits on who can touch the production controls.
That analogy is useful, but do not let it oversimplify the work. A mature IAM program can include privileged roles, just as some PAM platforms provide identity lifecycle features. The real line is operational intent. IAM manages identity at scale. PAM applies higher scrutiny to elevated access because the blast radius is larger.
What IAM should solve
IAM is usually the first identity capability an organization needs to get under control. It creates a consistent way to manage workforce, contractor, partner, and sometimes customer identities across on-premises infrastructure, SaaS platforms, cloud services, and business applications.
A practical IAM program typically covers identity lifecycle management, authentication, authorization, role design, federation, single sign-on, and multifactor authentication. When an employee joins, changes departments, or leaves, IAM should make access follow that event instead of relying on a chain of emails, tickets, and crossed fingers.
The operational outcomes are straightforward. Users get the access needed for their role faster. Departed users lose access reliably. Application owners stop managing disconnected local accounts. Security teams gain a better view of who can reach sensitive systems. Compliance evidence becomes less of an archaeological dig.
IAM is especially valuable when a customer has grown through acquisitions, adopted SaaS aggressively, or operates multiple identity stores with inconsistent controls. Those environments often have duplicate accounts, stale group memberships, shared credentials, and manual provisioning processes that burn help desk time while creating risk.
But IAM alone does not necessarily control how a privileged administrator uses elevated rights. An engineer may authenticate through single sign-on and multifactor authentication, then enter a production environment with standing admin privileges. The identity is validated. The session is still more powerful than it needs to be.
What PAM should solve
PAM reduces the risk attached to privileged credentials and privileged sessions. It does this by removing unnecessary standing access, securing passwords and secrets, approving access when appropriate, recording activity, and enforcing short-lived elevation.
Consider a common customer scenario: a senior systems engineer needs to troubleshoot a production server at 2:00 a.m. The engineer may need administrator rights, but only for a specific system, only for a short time, and only to perform a defined task. PAM can provide that access just in time, broker the session without exposing the password, and create an audit record of what occurred.
That is materially different from assigning the engineer permanent membership in a highly privileged group because it is convenient. Convenience has a habit of becoming permanent. Attackers know it.
PAM programs commonly address privileged account discovery, credential vaulting and rotation, session management, just-in-time access, privilege elevation, secrets management, break-glass controls, and third-party access. The exact scope depends on the environment. A cloud-native organization may prioritize privileged roles, API keys, and machine secrets. A healthcare provider with legacy infrastructure may need to start with Windows service accounts, vendor remote access, and domain administration.
PAM can add friction, and that is a feature only when the friction is proportional to the risk. Requiring a documented approval for every low-risk administrative action can slow operations into the ground. Giving every administrator unrestricted, permanent access creates the opposite problem. Good PAM design distinguishes between routine support, high-impact production work, emergency recovery, and automation.
Where PAM and IAM work together
The cleanest way to think about PAM and IAM is as connected control layers. IAM verifies the person and provides the normal access path. PAM governs the elevated access that must be tightly constrained, monitored, or temporary.
For example, IAM may authenticate an MSP engineer through the partner’s identity provider, enforce multifactor authentication, and confirm that the engineer belongs to the managed services team. PAM then determines whether that engineer can administer a specific customer tenant, whether approval is required, how long the elevation lasts, and whether the session is recorded.
This integration matters for channel delivery. A shared admin account is not a support model. It is an incident report waiting for a date and time. Named identities, role-based entitlements, customer-specific boundaries, and traceable elevation let a provider deliver responsive service without making customer trust dependent on informal process.
The same principle applies to automation. Scripts, integration accounts, and CI/CD pipelines need identities too. IAM can establish the identity and authorization model, while PAM or secrets management capabilities secure credentials, rotate secrets, and prevent hard-coded keys from quietly spreading across repositories and servers.
How to decide where to start
Start with the problem that creates the most immediate operational or security exposure, not the product category that happens to be popular this quarter.
If user onboarding takes days, offboarding is inconsistent, applications use separate credentials, and multifactor authentication coverage is uneven, IAM is likely the priority. Those weaknesses affect nearly every user and create a broad attack surface.
If the organization cannot tell who has domain admin rights, vendors use shared remote credentials, service account passwords have not changed in years, or cloud administrators hold permanent global privileges, start with PAM. A compromised privileged account can turn a contained event into a full-environment failure very quickly.
Many organizations need both, but they do not need a giant, all-at-once identity program. A staged approach is usually more durable. Establish a usable identity source and strong authentication. Identify privileged accounts and eliminate the riskiest shared or unmanaged credentials. Introduce vaulting, session controls, or just-in-time access for crown-jewel systems. Then expand into role governance, lifecycle automation, application integration, and nonhuman identity controls.
This is where assessment work earns its keep. Before deploying another platform, map identity sources, trust relationships, privileged groups, service accounts, remote access paths, cloud roles, and emergency procedures. The ugly parts of the environment are usually not hidden in the tool configuration. They are hidden in exceptions, tribal knowledge, and accounts nobody wants to own.
Design for operations, not a demo
A PAM or IAM project fails when the controls look good in a workshop but cannot survive an outage, an acquisition, or an after-hours support call. The design must account for operational reality.
Define emergency access before an emergency. Break-glass accounts should be protected, monitored, tested, and usable when the identity provider or network is unavailable. Determine who approves elevation, what evidence is retained, and how access is revoked when a technician changes roles. For managed service delivery, establish clear customer boundaries and a model for delegated administration that protects both parties.
Also measure outcomes that matter. Track standing privileged accounts removed, dormant accounts disabled, time to provision access, time to revoke access, multifactor coverage, privileged session coverage, and exceptions still requiring manual handling. Those metrics make the program defensible to security leadership and useful to operations leadership.
PAM and IAM are not interchangeable, and neither is a silver bullet. IAM gives organizations a disciplined way to manage identities at scale. PAM puts tighter guardrails around the accounts and sessions that can cause the most damage. Build them as connected capabilities, test them under real operating conditions, and your team gets something better than a compliance checkbox: controlled access that still lets the work get done when the pressure is on.